av-arcade-xss.jpg
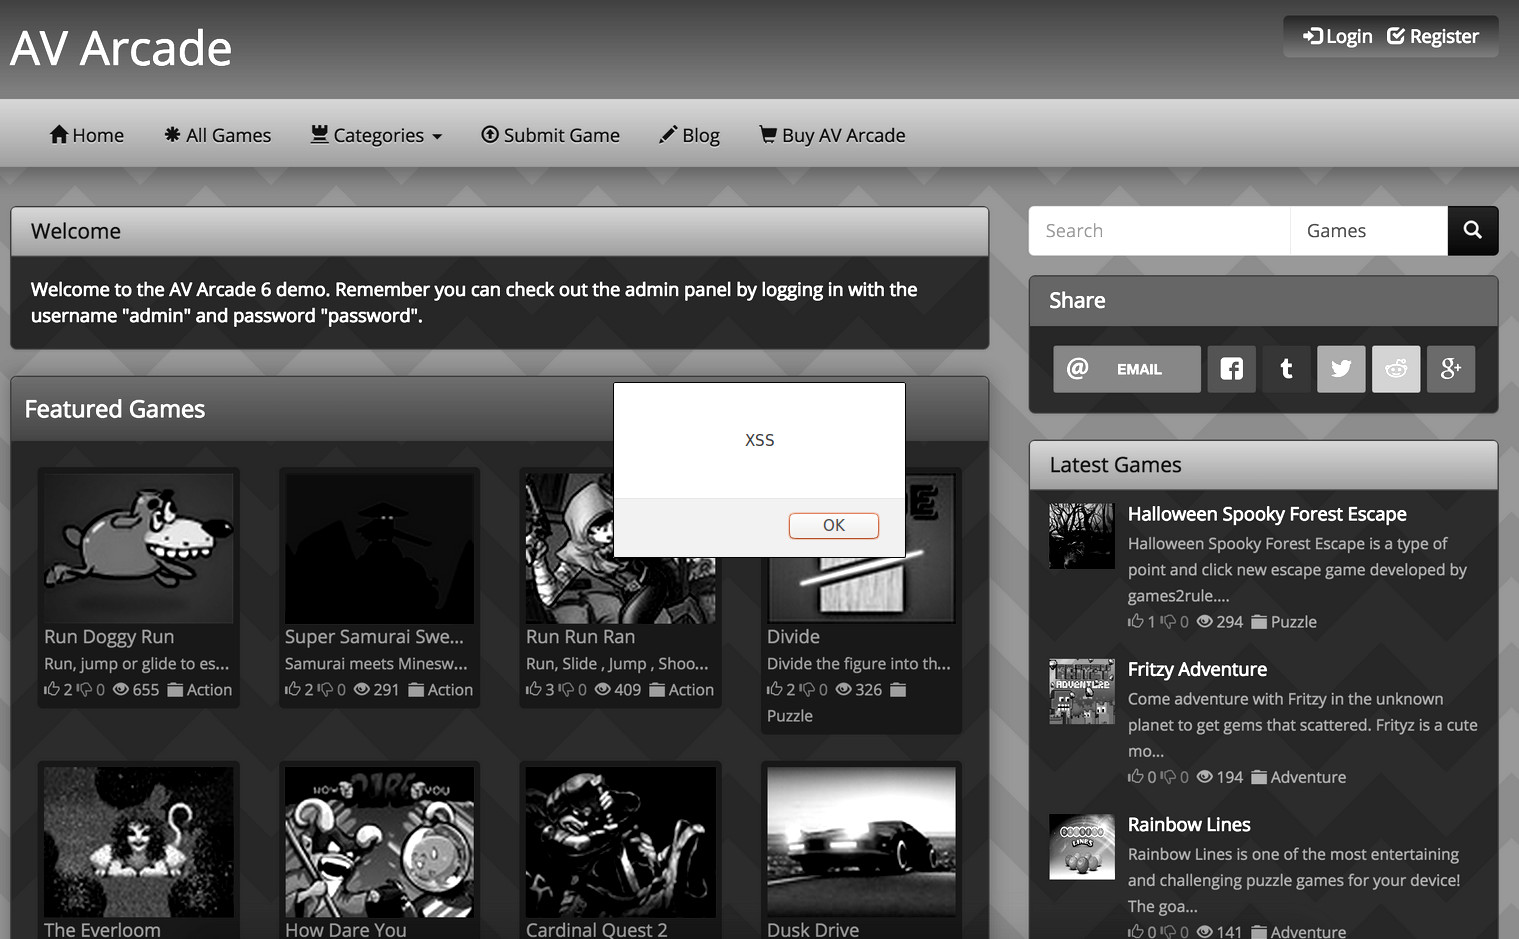
The Bug
AV Arcade's registration script stored the username field without sanitizing it, which could mean a malicious payload gets dropped into the username at signup would get rendered as-is wherever that username was later displayed.
This exploit impacted the member page and the arcade's homepage too.
That's a stored XSS bug: it doesn't need a victim to click a crafted link, it just sits in the database and fires for anyone who views the affected page. This has since been patched, but the write-up is kept here for reference.
The Fix
Two files edits are needed to protect against this exploit. Filter possible injections in the username before it's used or displayed anywhere:
register.php
PHP
register.php
find:
$username = htmlspecialchars($username);


add below:
$username = htmlspecialchars($username);
admin/manage_users.php
PHP
admin/manage_users.php
find:
while($row = mysql_fetch_array($sql)){

add below:
$username = htmlspecialchars($username);
Check for Existing Damage
If your install was already live before applying this fix, search your member list for any usernames that contain code and remove those accounts.